CONFIDENTIAL
REMOTE
COMPUTING
AN EDUCATION IN IMPERFECTION

TRAINING & CERTIFICATION

Hardware Roots of Trust, Remote Attestation and Trusted Execution

Two intensive days, 16 hours, aligned with the Oxford course

or email hello@kuc.uk · Download the flyer (PDF)

TPM 2.0 · SRTM/DRTM · Measured boot · Remote attestation · Sealing · TEE · SGX/TDX · TrustZone · Confidential VMs · TCB minimisation · Security by design

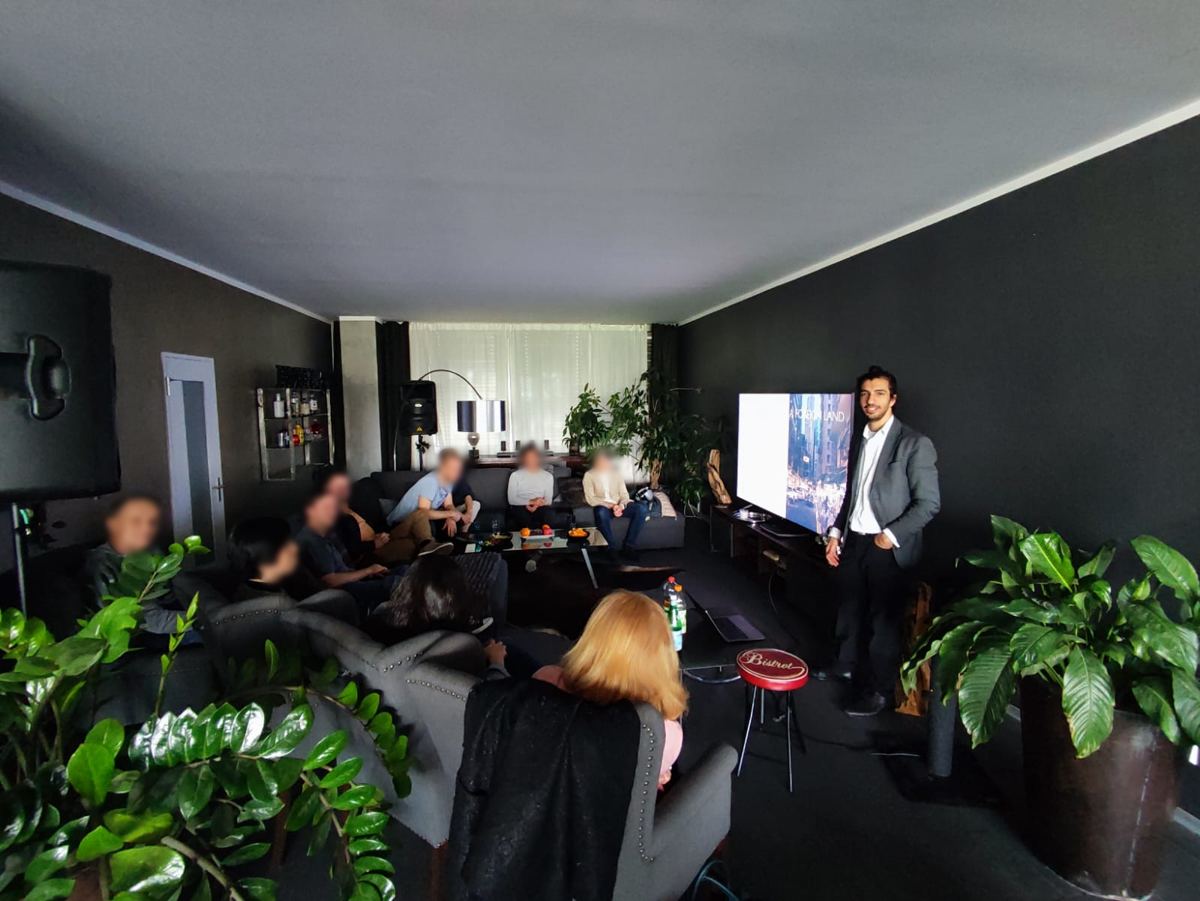
Dr Küçük presenting to a meetup group seated around the room
Startup office, Zürich · this could be your company
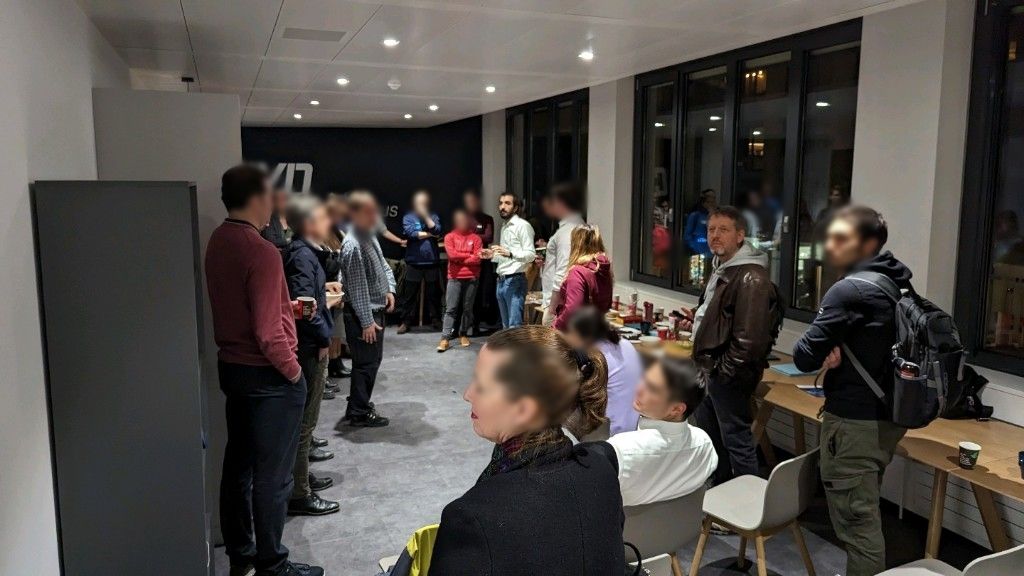
Guests talking in groups at an evening meetup
Cyber-Defence Campus, armasuisse · hosted on their premises, 70+ participants
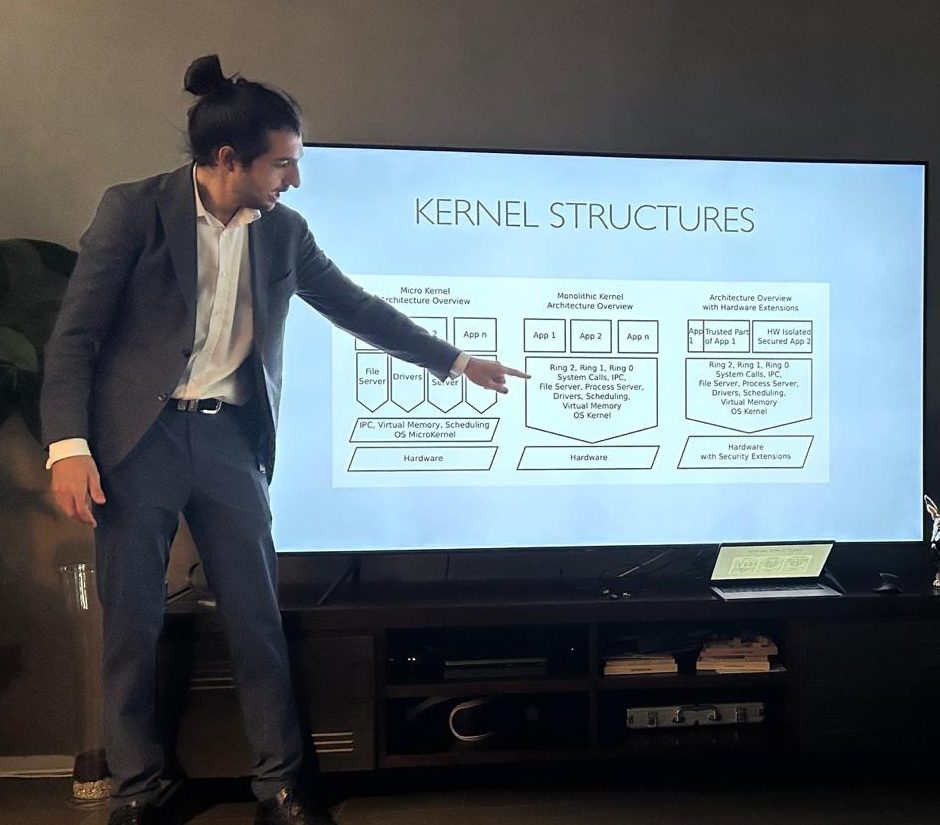
Dr Küçük pointing at a slide on kernel structures and hardware security extensions
Startup office, Zürich · host the next meetup at your company
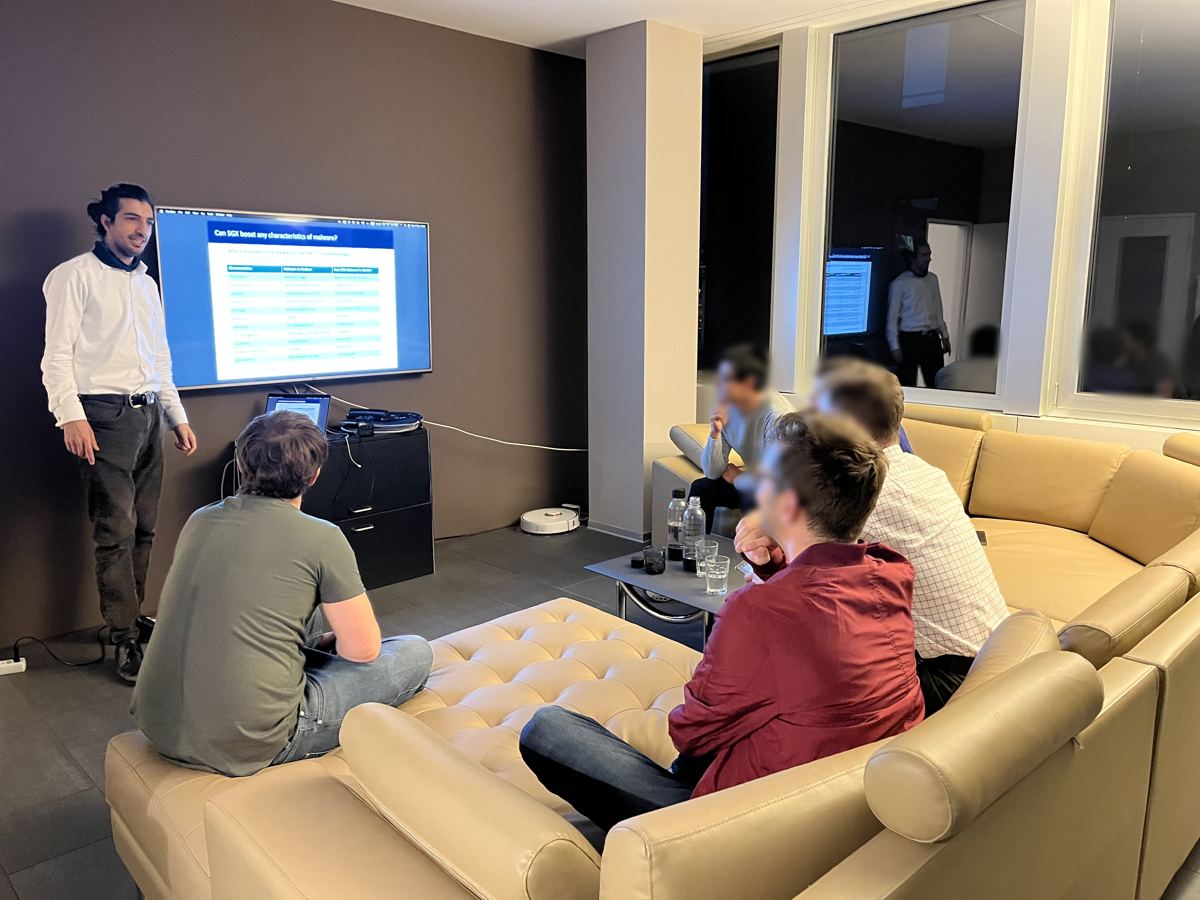
Dr Küçük at a meetup next to a slide on Intel SGX
Startup office, Zürich · this could be your company
Meetup guests in the main hall of ETH Zürich
ETH Zürich, Hauptgebäude · funded by the ETH Secure & Trustworthy Systems Group (SECTRS)
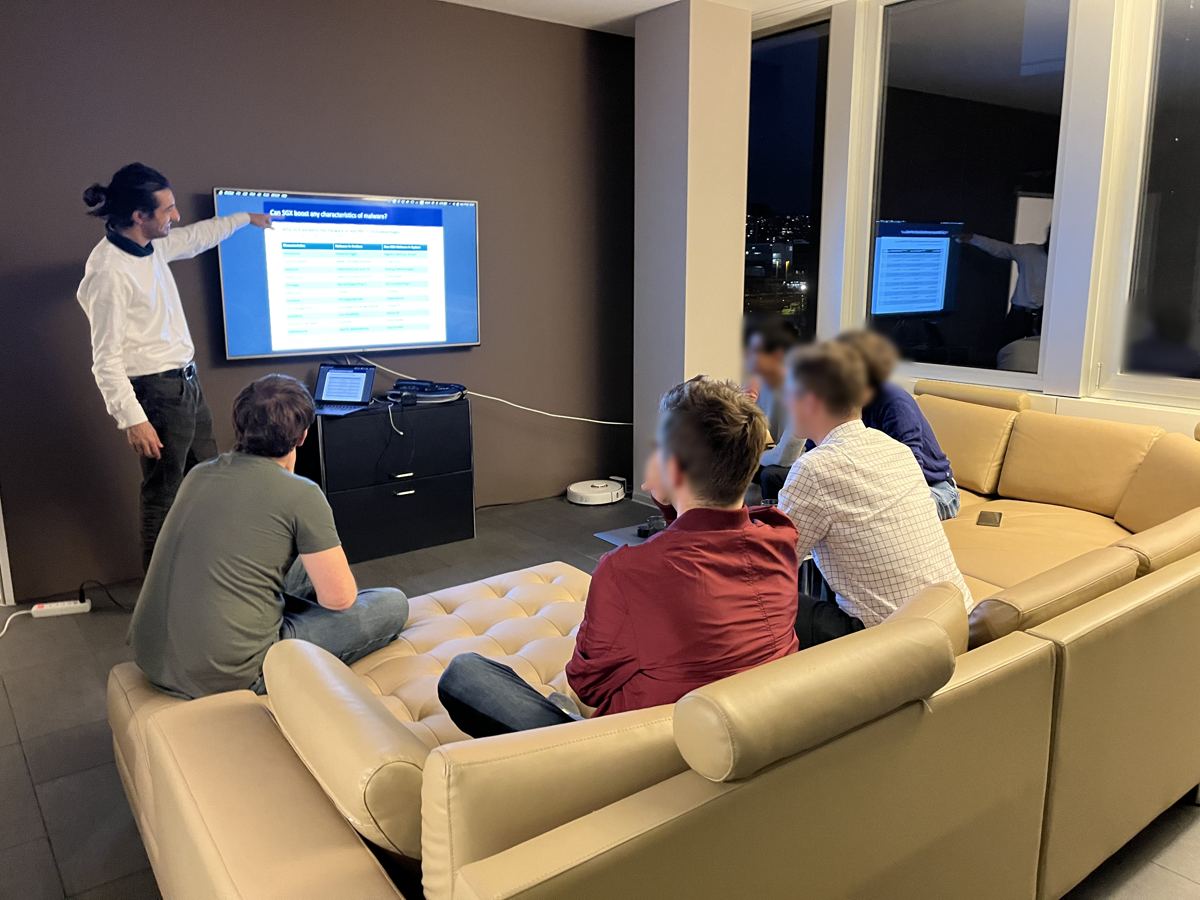
Dr Küçük pointing at a slide while meetup guests on a sofa follow along
Startup office, Zürich · host the next meetup at your company
Meetups

Informal evening talks on trusted execution environments, remote attestation and confidential computing.

Why this training

Build the skills to design, evaluate and ship systems that run on trusted hardware

Every modern platform ships a root of trust: a TPM, a CPU enclave, a secure monitor, a confidential virtual machine. Few engineers can say what those components actually guarantee, how to prove a remote machine is in a known state, and where the trust chain breaks.

This course closes that gap. It is aligned with the Trusted Computing Infrastructures curriculum taught at the University of Oxford, condensed into two intensive days for practitioners, with worked examples from real platforms instead of vendor marketing.

  • Taught by the author of the paradigmDr Küçük defined Confidential Remote Computing in his Oxford doctoral research, funded by Intel Corporation, and has taught trusted computing at Oxford.
  • Platform-level depthWhat the hardware does, instruction by instruction, from the first fetch after reset to a verified remote attestation. No slideware abstractions.
  • Immediately applicableSecurity by design in practice: threat models, trust-chain diagrams, TCB minimisation and a practical guide to zero trust, for your next architecture review, product requirement or audit.
  • Interactive and certifiedWorked examples and open discussion in a group of at most six, with a Certificate of Completion for every participant.
2 intensive days
09:00–17:00, 16 hours
Max. 6
participants per course
In person
in Zürich or at your premises
Certificate
with individual credential ID

Course programme

One course, two full days (09:00–17:00, 16 hours), aligned with the thirteen lectures of the Oxford course.

Day 1

Foundations of Trusted Computing

Trust basics and definitions, chains and roots of trust, the trusted platform (elements, threats, use cases), TPM 2.0 (keys, seeds, sealing, binding, authorisation policies), static and dynamic roots of trust for measurement (SRTM, DRTM, Intel TXT), trusted, measured and verified boot, measurement logs and PCRs, local and remote attestation, attestation identity keys and privacy, provisioning.

Day 2

Trusted Execution and Confidential Computing

Trusted execution environments as reference monitors and TCB minimisation, hardware isolation and rings, malware and rootkit resistance, Intel SGX enclaves (memory protection, keys, attestation, TCB recovery, Boot Guard), Arm TrustZone, virtualisation and guest attestation, a brief look at confidential virtual machines (Intel TDX, AMD SEV-SNP, Arm CCA), device ownership, integrity measurement, applications (disk encryption), and the language of trust: what an attestation can and cannot tell you.
Flyer

Take the course details with you

Two pages: why this training, the programme, your instructor and the course details. Easy to share with your team or your manager.

Flyer page 1: Training and Certification, why this training, key facts Flyer page 2: course programme, content focus, audience, instructor, course details and contact

Content focus

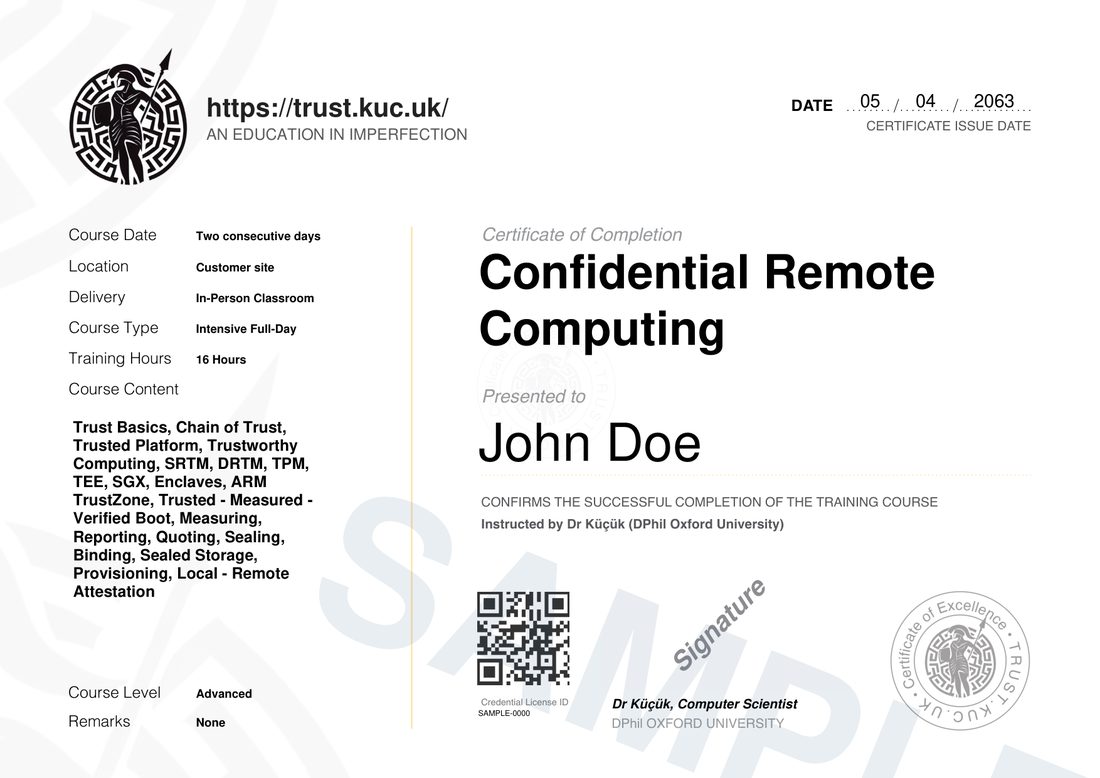
As printed on the certificate, the course covers:

  • Trust basics, chain of trust, roots of trust
  • Trusted platform and trustworthy computing
  • SRTM, DRTM, Intel TXT
  • TPM 2.0: measuring, reporting, quoting
  • Sealing, binding, sealed storage
  • Trusted, measured and verified boot
  • Local and remote attestation
  • Provisioning and device identity
  • TEE, SGX enclaves, Arm TrustZone
  • Confidential VMs: TDX, SEV-SNP, CCA

Who is this training for?

Engineers and decision-makers who build on, buy or audit trusted hardware:

  • Security and platform architects
  • Firmware and embedded engineers
  • Cloud, virtualisation and kernel engineers
  • Product security and PSIRT teams
  • Confidential AI and data-platform teams
  • Security consultants and auditors
  • CISOs, CTOs and technical product owners

Prerequisites: working knowledge of operating systems and computer architecture. No prior trusted-computing experience required.

Dr Küçük speaking at a meetup

Your instructor

Dr Küçük holds a DPhil in Computer Science from the University of Oxford and has taught at Oxford, including Trusted Computing Infrastructures. Received PhD funding from Intel Corporation for SGX/TEE research.

He defined the Confidential Remote Computing paradigm in his Oxford doctoral research and released it openly for anyone to build on: doi:10.5287/ora-2rovaxbjd.

Software engineer and security architect. Completed two Innosuisse projects at ETH Zürich, where he was previously affiliated with ETH D-INFK and ETH D-MAVT.

Published researcher and speaker at Black Hat Europe and DEF CON; adviser to industry on trusted hardware, attestation and confidential computing.

Course details

Participants
Max. 6 per course
Duration
2 intensive days, 09:00–17:00
Language
English
Level
Advanced
Location
In person, in Zürich or at your premises
Certificate
Certificate of Completion with an individual credential ID, per participant
Consulting
For certified participants: commercial products, architecture, and formal verification of products and protocols
Sample Certificate of Completion for the Confidential Remote Computing course, marked SAMPLE
Sample certificate

Contact

Bring trusted computing and confidential computing into your team now and apply it in your next product.

Participant feedback

What participants say

Complex ideas, explained simply

Senior engineer

“I have never had a lecture on TEEs and SGX without a single technical word, only everyday analogies. I enjoyed it so much and understood everything. I am still surprised such complex concepts can be explained in plain language, without jargon.”

A roller coaster, in the best way

Course participant

“The course is like a roller coaster: sometimes super technical, sometimes everyday examples from daily life. Very practical and very relevant to today’s issues. It lit up many dark areas I never understood in systems, security, networking and software. A very powerful intersection of them all.”

The skills that got me a new job

Senior security architect

“I could not understand how keys can be generated inside an enclave at all. When the depth of the concept finally clicked, I was honestly shocked. I learned so much about key management and binding keys to software identity during execution, and those concepts got me a new job at ABB.”

More than I expected

Course participant

“I came in insecure and not confident at all, and left confident and knowledgeable. The teacher makes sure every detail is covered and notices quickly when someone has not understood something. I never expected to understand these advanced topics, and I am very happy that I did.”

Oxford-level content, in our company

Corporate client

“We were very lucky to get a spot. This content is otherwise only taught in Oxford’s master’s programme in computer science, which would cost a fortune. This course brings it directly to our company.”

Swisstronik

The first company to receive Confidential Remote Computing certification outside academia.

On their CTO and Blockchain Lead completing the course

“An invaluable experience for our team.”